Future-proof your infrastructure: Achieve quantum resistance with BIG-IP LTM
Prepare your critical infrastructure for the quantum computing era by implementing post-quantum cryptography (PQC) to protect against emerging harvest now, decrypt later (HDNL) threats.
The quantum threat to today's encryption
For decades, organizations relied on public-key cryptography to secure digital communications and protect sensitive data. However, the rise of quantum computing threatens to render these established encryption methods obsolete. Malicious actors are already engaging in harvest now, decrypt later (HNDL) attacks, capturing and storing encrypted data today with the intention of decrypting it once a sufficiently powerful quantum computer becomes available—an event known as “Q-Day.”
This poses a significant risk to organizations, especially those in the finance, healthcare, government, and defense sectors, where data must remain secure for years or even decades. The transition to a new generation of quantum-resistant cryptography is not a distant concern, as the estimated timeline to Q-Day shrinks every year. This makes post-quantum readiness an urgent priority for protecting long-term data, maintaining regulatory compliance, and ensuring the integrity of critical digital infrastructure.
For NetOps and Platform Ops teams, the challenge comes in implementing these next-generation security protocols without disrupting application performance or availability.
Malicious actors are capturing encrypted data today and planning to decrypt it with future quantum computers, putting long-term data for finance, healthcare, and government at immediate risk.
Build a quantum-ready future with BIG-IP LTM
F5 BIG-IP LTM provides a strategic control point to begin the journey toward quantum readiness. By acting as a crypto-agile proxy, BIG-IP LTM enables organizations to seamlessly implement post-quantum cryptography (PQC), protecting applications and data without requiring immediate, complex changes to backend application servers. This approach allows you to build a bridge from today’s classical cryptography to a quantum-resistant future.
Starting with BIG-IP v17.5, you can implement client-side PQC, and with v17.5.1, you can enable full client- and server-side PQC. This is achieved using a hybrid key exchange mechanism, which combines a classical cipher with a new, quantum-resistant algorithm like ML-KEM (Kyber), a finalist in the NIST PQC standardization process. This hybrid approach ensures protection against both classical and quantum attacks, providing a reliable defense during the cryptographic transition.
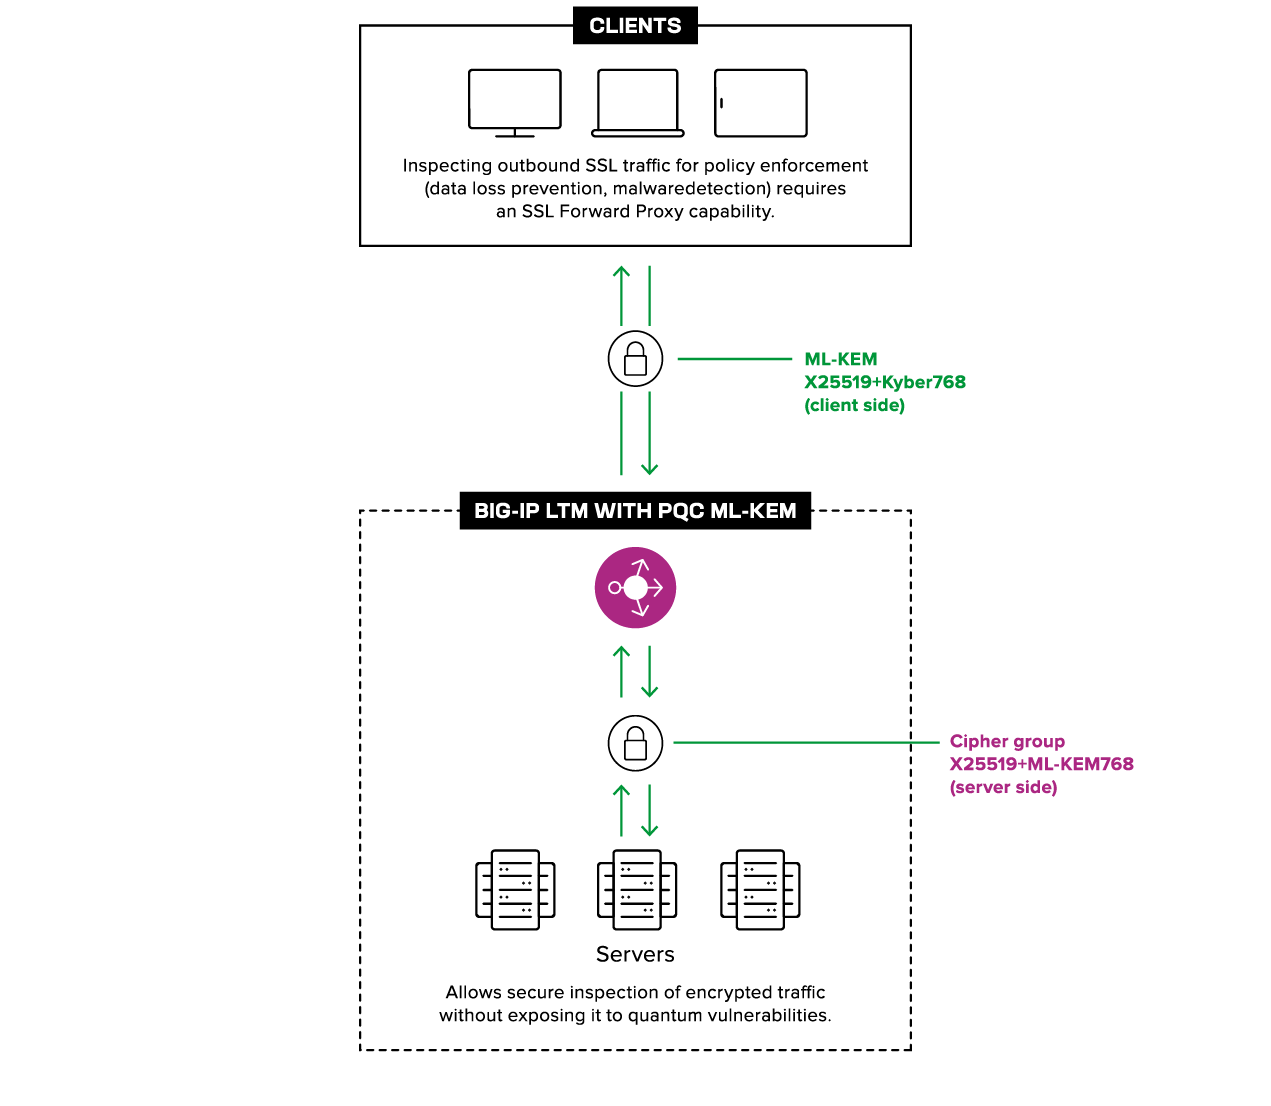
The role of BIG-IP LTM as a PQC intermediary is critical for a phased rollout. It can terminate traffic encrypted with a hybrid, quantum-resistant cipher at the edge and then re-encrypt it using a classical cipher that internal servers understand. This decouples your external security posture from your internal infrastructure, allowing you to strengthen security for external traffic immediately while planning internal upgrades at your own pace.
BIG-IP LTM acts as a crypto-agile proxy, enabling you to deploy hybrid quantum-resistant encryption without requiring immediate changes to your backend application servers.
An application-first approach to quantum readiness
The threat of quantum computing requires a proactive and strategic response. Waiting until the threat is fully realized is not an option. F5 BIG-IP LTM empowers infrastructure teams to address the quantum challenge head-on by integrating post-quantum cryptography into existing application delivery architecture.
By leveraging BIG-IP LTM's crypto-agility and strategic position in the data path, you can protect your organization from HDNL attacks, prepare for emerging compliance standards, and ensure the long-term security of your most valuable data, all while maintaining the performance and reliability your users expect.
Key benefits
Protect long-term sensitive data
Neutralize harvest now, decrypt later threats to secure data with a long shelf life, crucial for finance, healthcare, and government sectors.
Ensure future-ready compliance
Align with emerging mandates for quantum-resistant cryptography and build a crypto-agile architecture that adapts to evolving standards.
Maintain performance and availability
Implement next-generation, quantum-resistant ciphers without sacrificing the performance and reliability of your application delivery services.
Bridge the crypto-generation gap
Serve as a PQC intermediary, enabling quantum-resistant encryption for external traffic while maintaining classical encryption for internal application servers.
Key features
Hybrid key exchange support
Combines a classical algorithm (like X25519) with a quantum-resistant NIST-selected algorithm (ML-KEM/Kyber) for robust, dual-layer protection during the transition period.
Client and server-side PQC
Supports client-side PQC starting in BIG-IP v17.5 and extends to full client and server-side proxy support in BIG-IP v17.5.1.
Crypto-agile architecture
Leverage BIG-IP LTM's flexible architecture to rapidly adopt new PQC algorithms as they are standardized, minimizing operational disruption.
Hardware-accelerated performance
Utilize advanced hardware offload capabilities to mitigate the performance impact of computationally intensive PQC algorithms.