Q-Day, the Quantum Deadline & Post-Mythos AI Risks: Is Your Organization Prepared?
Date: 24 November 2026, Tuesday
Time:
11:00 AM–12:00 PM SGT (GMT+8)
10:00 AM–11:00 AM ICT (GMT+7)
Format: Live Virtual Briefing & Interactive Q&A
Duration: 60 minutes
Register now
Across ASEAN, rapid growth in cross-border payments, critical digital infrastructure, and multi-cloud ecosystems is increasing both the value and the lifespan of sensitive data. As the stakes rise, organizations are reaching a dual security inflection point:
- The quantum threat horizon: Cybercriminals and nation-state actors can harvest encrypted, high-value information today and decrypt it later when quantum computing becomes viable - placing intellectual property, financial transactions and sovereign citizen data at long-term risk.
- The post-Mythos AI reality: Autonomous, machine-speed AI adversaries are accelerating vulnerability discovery, cryptographic flaw identification and zero-day exploit chaining beyond the pace of traditional patching and governance cycles.
Every delay compounds organizational risk. Proactive preparation must begin today.
In this session, we'll explore:
The Dual Threat Convergence: Why the combination of "Harvest Now, Decrypt Later" (HNDL) and machine-speed Post-Mythos AI offensive agents demands immediate architectural modernization.
ASEAN Regulatory Landscapes: Key insights into national AI Risk Management & Post-quantum cryptography (PQC) roadmaps, compliance timelines and emerging cryptographic governance mandates across the region.
Navigating the AI Frontier: Actionable strategies to secure legacy application architectures and modern AI models against Q-Day risks and machine-speed AI threats.
PQC Readiness & AI Risk Management: How to evaluate your organization’s cryptographic posture, assess AI risk exposure and build a resilient migration strategy.
Who should attend:
- Chief Information Security Officers (CISOs), CIOs, and Chief Risk Officers
- Heads of Enterprise Architecture, Infrastructure, Cloud, and Cybersecurity
- GRC, compliance, and technology leaders in regulated sectors, including banking and financial services, government, telecommunications, and healthcare
Presenters
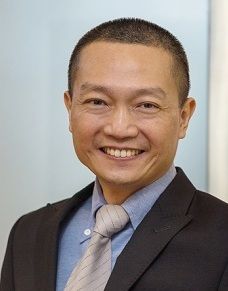
Chin Lim
Senior Director for ASEAN, F5
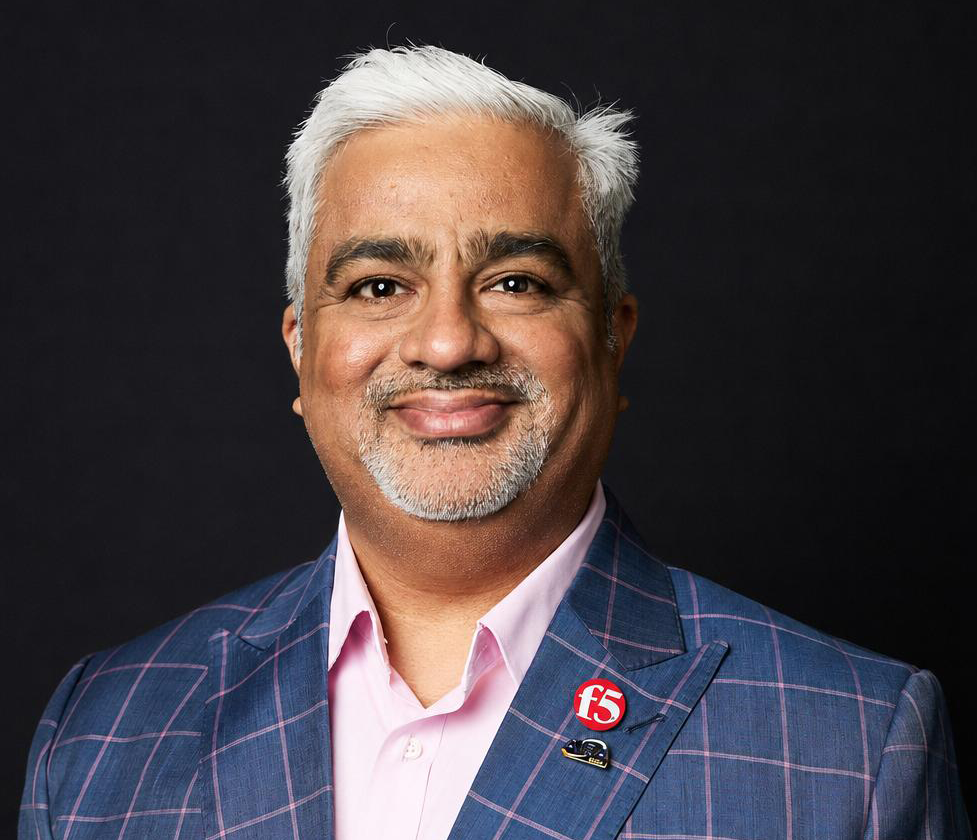
Abbas Kudrati
Field CISO for APCJ
F5