Zero trust architecture for government
Protect government applications, APIs, and AI with zero trust across hybrid multicloud environments.
Safeguard mission continuity and citizen trust
Build resilience for mission-critical services
F5 combines security controls with intelligent traffic management and resilient infrastructure design to prevent downtime from cyber incidents and speed recovery when they occur. Agencies sustain continuity of operations under attack, keeping mission data protected and essential services available.
Protect critical services with AI-powered security
F5 delivers consistent and continuous inspection of model, agent, and API traffic, detecting shadow AI and unmanaged APIs across hybrid multicloud and air-gapped environments, and blocking unauthorized data flows, prompt injection, and data leakage before they reach sensitive citizen or mission data.
Simplify security operations
F5 centralizes policy management, visibility, and automation across hybrid multicloud environments. Agencies cut tool sprawl, streamline security operations, and act on L3 through L7 telemetry for faster root cause analysis and improved MTTR.
Digital sovereignty and simplified compliance
F5 logs every policy and enforcement decision, creating an evidence trail that demonstrates zero trust maturity against NIST SP 800-207, the CISA Zero Trust Maturity Model, and equivalent national frameworks. Control mapping extends to baselines such as NIST 800-53. For nations with data residency requirements, sovereign deployment options keep control local, and F5 enforces zero trust inside those boundaries.
AI-powered protection with granular zero trust controls
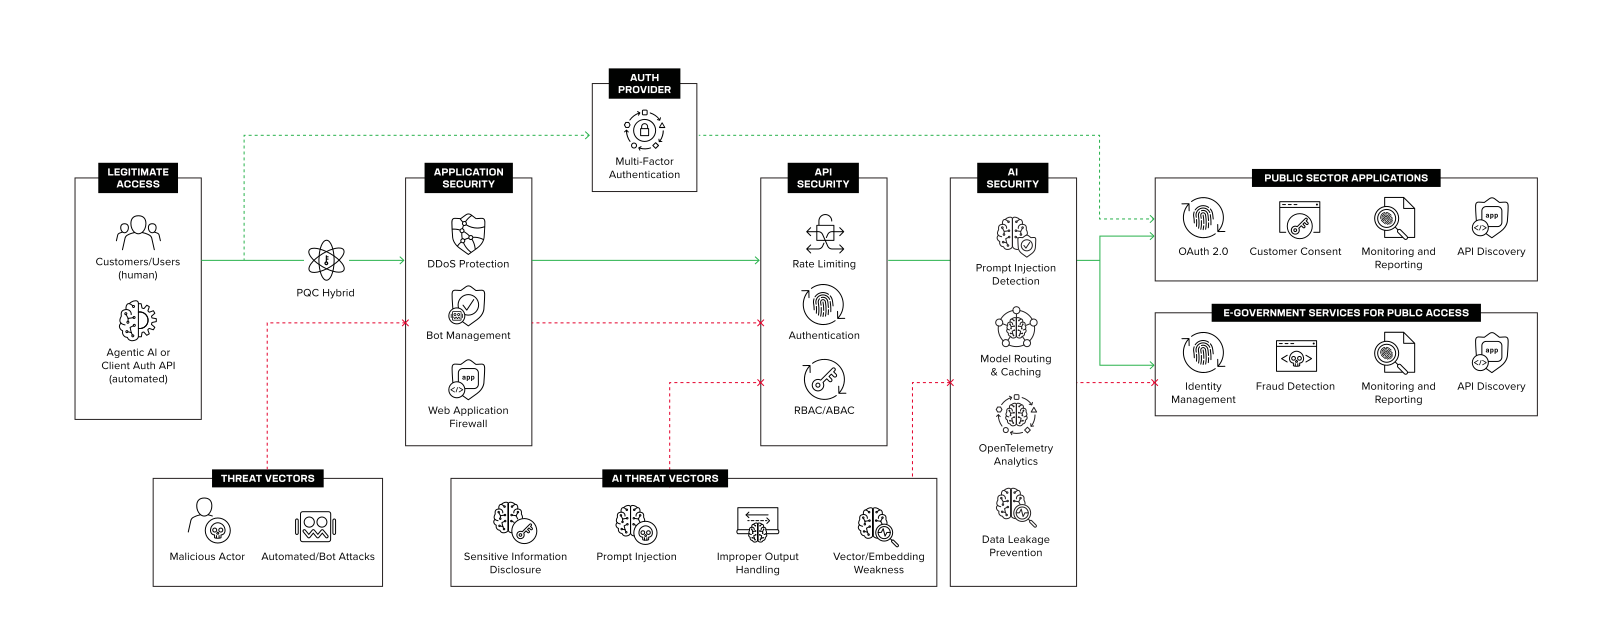
Consistent and continuous protection for workloads across hybrid multicloud
The F5 Application Delivery and Security Platform (ADSP) enforces cybersecurity in the application traffic path across data center, cloud, and edge, with zero trust at its core: identity-aware access, micro-segmentation, encrypted traffic inspection, and app and API runtime protection. The F5 AI Security Platform extends that foundation to AI workloads, discovering shadow AI and governing model, agent, and API traffic, deployable down to air-gapped environments. Policies and logs from both platforms provide audit evidence required to demonstrate compliance.
How F5 helps
Identity and access management
Secure modern and legacy applications with zero trust
Enable identity-aware zero trust access with centralized policy enforcement for modern and legacy applications using consistent access controls.
BIG-IP Zero Trust Access
Secure identity-aware access for government applications with policy-based controls.
Distributed Cloud Client-Side Defense
Protect government web applications from malicious client-side attacks.
Network firewall and micro-segmentation
Strengthen network security with encrypted traffic visibility
Enable centralized SSL/TLS visibility for encrypted threat inspection, apply policy-based traffic controls, and strengthen micro-segmentation to mitigate DDoS and network threats.
BIG-IP SSL Orchestrator
Decrypt encrypted government traffic for security inspection.
Network Firewall Security Management
Apply policy-based traffic controls to strengthen network security and DDoS protection.
Application and AI runtime protection
Enable consistent security across digital services
Protect government applications, APIs, and AI with API lifecycle security, policy-driven access controls, and AI guardrails across distributed environments.
API Security
Discover, monitor, and secure APIs with continuous visibility and governance.
Web Application Firewall
Protect applications from Layer 7 attacks and OWASP Top 10 risks.
NGINX API Gateway
Secure API communication with policy-driven authentication and access controls.
AI Guardrails
Govern AI interactions to help reduce prompt injection and data exposure.
Continuous visibility and unified management
Standardize application delivery and security operations
Reduce operational complexity with centralized management, end-to-end visibility, and intelligent automation for application delivery and security.
BIG-IQ Centralized Management
Manage BIG-IP devices and services through a single, unified management platform.
BIG-IP Automation Toolchain
Automate BIG-IP provisioning and configuration with declarative interfaces.
Nginx One
Consolidate app delivery, security, and management into one offering for consistent operations.
F5 Insight For ADSP
Unify application and infrastructure visibility with actionable operational intelligence.
Resources
Analyst reports
Solution overviews
SOLUTION OVERVIEW
F5 Zero Trust Architecture Solutions
SOLUTION OVERVIEW
Zero Trust in an Application-Centric World
SOLUTION OVERVIEW