AI is accelerating everything: new model endpoints, new data pipelines, new agent-to-agent traffic patterns, and new attack surfaces. Most enterprises are meeting it with infrastructure that was never designed for it. According to the F5 2026 State of Application Strategy Report, 86% of enterprises now run applications across on-premises data centers, public cloud, and colocation environments.
That flexibility comes at a cost. Every environment adds another delivery and security stack to configure, secure, and monitor, creating configuration sprawl and policy gaps. Every one of those environments typically runs its own application delivery and security solutions, has its own configurations, and enforces its own policies.
That solution and policy fragmentation was already a headache to manage when application delivery meant routing HTTP traffic to web servers. AI raises the stakes. Data has to move faster, security has to scale with the workload, and no operations team can afford a different toolset for every environment.
“F5 BIG-IP Virtual Edition (VE) on Equinix Network Edge applies one consistent set of delivery, security, and observability policies to every traditional and AI application, from the data center to the cloud.”
Data volumes for training, fine-tuning, and retrieval-augmented generation (RAG) are an order of magnitude larger than traditional application traffic. Inference endpoints need low-latency, predictable routing to increase their performance while reducing inference costs. Autonomous agents are starting to talk to each other using protocols like MCP, generating traffic that traditional perimeter web application firewalls (WAFs) can’t inspect.
Application delivery controllers (ADCs) are meant to solve exactly this. In practice, the hybrid multicloud infrastructure approach also means many enterprises have multiple ADCs across their environments and legacy ADC hardware approaching end-of-support.
Three challenges reshaping app delivery
Most application delivery strategies today are facing three large challenges that will only continue to grow over the next few years. They are:
- Operational complexity. Every data center, cloud, and edge site tends to run a different ADC configuration, a different automation pipeline, and a different monitoring setup. Configuration drift and inconsistent policy enforcement across an organization’s multiple environments is all too common.
- AI-specific delivery demands. AI data volumes are orders of magnitude larger, requiring massive throughput for model training, fine-tuning, and RAG, while inference endpoints require low-latency, predictable routing for better performance.
- Security gaps around AI and internal traffic. Most organizations have implemented protections for public-facing applications. However, far fewer have consistent protections for internal APIs, model-serving endpoints, and AI data pipelines which sit outside the reach of a typical perimeter web application firewalls.
Introducing F5 BIG-IP Virtual Edition on Equinix Network Edge
F5 BIG-IP Virtual Edition (VE) on Equinix Network Edge applies one consistent set of delivery, security, and observability policies to every traditional and AI application, from the data center to the cloud. Organizations that employ BIG-IP within Equinix's metro fabric, close to clouds and partners with private interconnection, can extend consistent Layer 4–Layer 7 application services across hybrid multicloud architectures.
Network Edge gives customers a way to stand up a digital point of presence globally, close to the clouds, users, and partners they need to reach, and connect it privately through Equinix Fabric. The outcome is applications that launch in new markets sooner, partners and acquisitions that come online faster, and users who get consistent performance wherever they are.
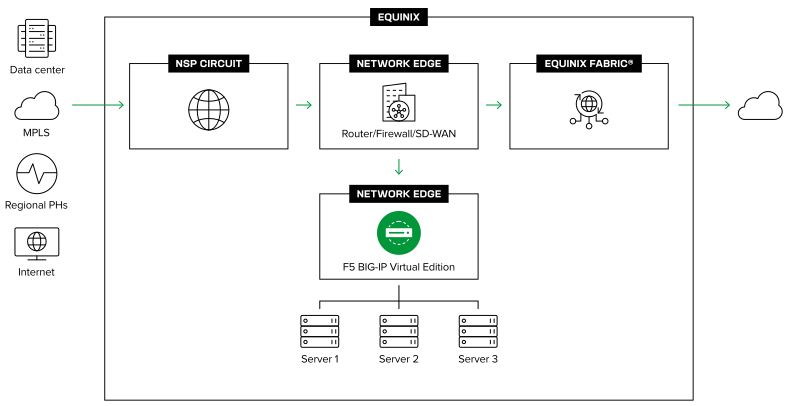
While BIG-IP VE isn't new, running it on Equinix Network Edge changes where it can run: Network Edge hosts the BIG-IP VE instance, and Equinix Fabric provides the private interconnection to your clouds, partners, and offices.
On Network Edge, BIG-IP VE delivers core application delivery—local traffic management, load balancing, SSL/TLS offload, and health monitoring—for traffic moving between those environments. Additional BIG-IP security modules can be licensed separately, and F5 Distributed Cloud Services , F5 NGINX Plus, and F5 AI Guardrails extend WAF, API protection, bot defense, DDoS mitigation, and zero-trust access across the same Equinix architecture.
Network Edge lets you place BIG-IP VE instances globally on demand, so a new digital point of presence can be added, changed, or retired as the business needs it, without a long-lived physical commitment. And having it all run on Equinix Fabric provides the private interconnection between that instance and your clouds, partners, and offices, bypassing the public Internet entirely for lower latency and better performance of demanding application and AI workloads. Together, F5 BIG-IP VE running on Equinix Network Edge deliver:
- Agility to expand and adapt. Market expansion, partner onboarding, M&A integration, and architectural change each call for a new digital point of presence, and each can be added, modified, or retired without heavy upfront investment. Shorter deployment times follow from that structural advantage rather than being the reason to choose the platform.
- Lower egress costs and more predictable performance. Private interconnection through Equinix Fabric keeps traffic off costly public paths and delivers lower latency needed for better application and AI performance.
- Easier, more consistent security. WAF, API protection, bot defense, DDoS mitigation, and zero-trust access can be applied consistently across all environments, whether the traffic is for a public-facing app, an internal API, or an AI pipeline.
- Standardized operations across every environment. The same policies, automation, and observability tools work the same way in the data center, in the cloud, and at the edge. The BIG-IP Automation Toolchain (AS3, Declarative Onboarding) drops into existing CI/CD and infrastructure as code (IaC) workflows, and F5 Insight for ADSP delivers end-to-end observability via OpenTelemetry.
- No forced rip-and-replace. Existing BIG-IP policies, iRules, and operational knowledge can be leveraged. Physical and virtual BIG-IP can run side by side under the same platform.
Building the F5 Application Delivery and Security Platform on Equinix
Adding BIG-IP VE fulfills another piece of the F5 Application Delivery and Security Platform (ADSP) that runs on Equinix, allowing customers to converge application delivery and security into one set of consistent services, from the edge to the cloud, so every app and API gets the same availability, security, and orchestration no matter where it lives.
As you probably know, F5 NGINX Plus, F5 Distributed Cloud, and F5 AI Guardrails already operate on Equinix, with NGINX and Distributed Cloud CE available as VNFs that can be deployed on Equinix Network Edge. Adding BIG-IP VE as a virtual network function provides the application delivery control layer to that architecture, giving you more F5 ADSP components to choose from depending on your deployment strategies and needs.
If you are already using BIG-IP, this is great news. You can now extend your existing policies and operational model into Equinix Network Edge-enabled metros without needing to learn a new solution.
Delivering applications and AI across hybrid multicloud infrastructure doesn’t need to lead to security complexity, multiple ADCs, or escalating egress costs from traffic tromboning through centralized hubs when you have proven F5 ADSP solutions like F5 BIG-IP VE running as part of a private, distributed, private interconnection architecture delivered by Equinix.
To learn more, visit our F5 and Equinix webpage. Also, check out our solution guide.
About the Author

Related Blog Posts
A new path to technical excellence for F5 partners
Introducing F5 Partner Foundations, a structured learning curriculum to build F5 partner engineer expertise with a clear pathway to specialization.
Secure-by-design storage for agentic AI: Why runtime visibility plus traffic control matters
Learn how F5 is collaborating with NVIDIA to help protect agentic AI with secure-by-design AI infrastructure, runtime visibility, and traffic control.
Why sub-optimal application delivery architecture costs more than you think
Discover the hidden performance, security, and operational costs of sub‑optimal application delivery—and how modern architectures address them.
Architecting for AI: Secure, scalable, multicloud
Operationalize AI-era multicloud with F5 and Equinix. Explore scalable solutions for secure data flows, uniform policies, and governance across dynamic cloud environments.
AppViewX + F5: Automating and orchestrating app delivery
As an F5 ADSP Select partner, AppViewX works with F5 to deliver a centralized orchestration solution to manage app services across distributed environments.

F5 NGINX Gateway Fabric is a certified solution for Red Hat OpenShift
F5 collaborates with Red Hat to deliver a solution that combines the high-performance app delivery of F5 NGINX with Red Hat OpenShift’s enterprise Kubernetes capabilities.